

One Control, Many Frameworks: How to Simplify Multi-Framework Compliance Management

Shambhavi Singh
October 23, 2026
Most organisations don’t answer to one regulator or one standard. A bank in the Gulf may work with SAMA requirements, ISO 27001 and ISO 22301 at once, while a technology provider serving European clients may add NIST and DORA on top. This is where multi-framework compliance management comes in.
Each framework arrives with its own checklist, its own language and its own audit cycle. The result is familiar: the same evidence collected three times, the same control tested by three teams, and a compliance calendar that never has a quiet month.
This is the real challenge of modern compliance management. The problem is rarely a lack of effort. It is a lack of connection. In this blog, we look at one narrow but powerful fix: building a unified control framework, so you map once and comply many times.
The Hidden Cost of Managing Frameworks Separately
When each framework is managed in its own spreadsheet or folder, three costs build up quietly.
Duplicated work. Many requirements overlap. Access control, incident response, vendor oversight, backup and recovery, and policy governance appear in almost every major framework. Without a shared view, teams treat each appearance as a new task.
Inconsistent answers. When the same control is described differently in each assessment, auditors notice. A control that is “fully implemented” in one report and “partially implemented” in another damages credibility.
Slow, stressful audits. Evidence lives in inboxes and shared drives. Before every audit, someone spends weeks hunting for screenshots, approvals and logs, hoping they are still current.
None of this makes the organisation more secure or more resilient. It only makes compliance heavier.
What Is Control Harmonisation?
Control harmonisation means defining your controls once, in plain language, and then mapping each control to every framework requirement it satisfies.
For example, a single control such as “access rights are reviewed quarterly by system owners” can support requirements in ISO 27001, NIST, SAMA and other frameworks at the same time. You test the control once, collect the evidence once, and reuse the result across every framework that applies.
This is often called control mapping, and it is the foundation of an efficient multi-framework compliance programme. It also shifts the question from “Which framework does this belong to?” to “Is this control working?”, which is the question that actually matters.
Five Signs Your Compliance Management Is Duplicating Effort
Check how many of these sound familiar.
1. The same evidence is requested repeatedly. Different auditors or teams ask for the same access review or policy approval, and each time it is collected from scratch.
2. Each framework has its own owner and tracker. Nobody can say how many controls you really have, because the count depends on whose spreadsheet you open.
3. Control owners don’t know which requirements they support. They see a task, not the regulatory obligation behind it, so they treat it as optional paperwork.
4. Findings are fixed in one framework but not another. A gap closed for ISO 27001 reappears in the SAMA assessment because the two were never linked.
5. Audit readiness depends on heroics. Preparation means a few people working late for a few weeks, rather than a process that runs all year.
If three or more apply, your compliance management is likely costing more than it should.
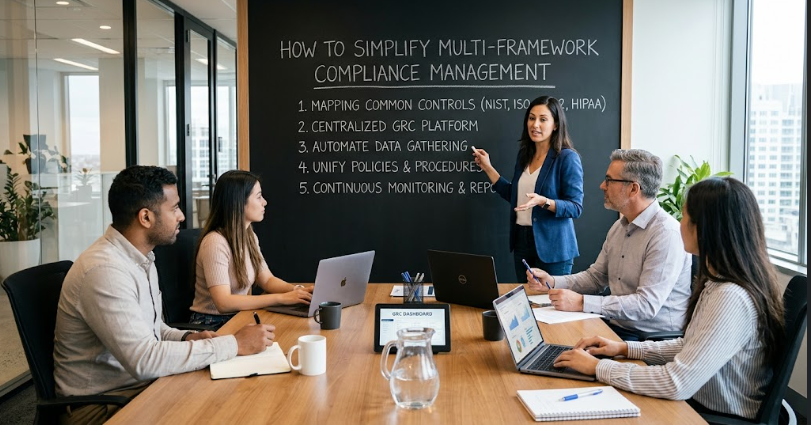
How to Build a Unified Control Framework in Five Steps
You don’t need to start from zero or overhaul everything at once.
Step 1: List the frameworks that genuinely apply. Include regulatory requirements, contractual obligations and voluntary standards. Be honest about which are mandatory and which are aspirational.
Step 2: Create one common control set. Consolidate overlapping requirements into a single library of controls with clear descriptions, owners and frequencies. Aim for controls that are specific enough to test and general enough to serve more than one framework.
Step 3: Map controls to requirements. For each control, record every framework clause it supports. Where a requirement has no matching control, you have found a genuine gap. Where a control maps to nothing, question whether it is needed.
Step 4: Assign owners and evidence once. Each control should have one accountable owner and a defined type of evidence, such as a log extract, an approval record or a test result. Evidence is collected against the control and reused across frameworks.
Step 5: Link findings to controls, not to frameworks. When an issue is found, it is recorded against the control, assigned an owner and a deadline, and re-tested after the fix. Every framework that depends on that control benefits from the same remediation.
This approach reflects a principle we often return to: a finding that is documented but not remediated is a lesson identified, not a lesson learned.
From Audit Season to Continuous Compliance
Once controls are unified, a bigger shift becomes possible: moving from periodic checks to continuous compliance monitoring.
Traditional compliance management is seasonal. Teams prepare intensely, pass the audit, and relax until the next cycle. The weakness is obvious. A control that passed in March may have drifted by September, and nobody notices until the next assessment.
Continuous monitoring changes the rhythm:
- Controls are tested on their defined frequency, not only before audits
- Evidence is gathered as work happens, not reconstructed later
- Overdue controls and expiring evidence trigger alerts to owners
- Leadership sees current compliance status rather than last quarter’s snapshot
The goal is audit readiness as a permanent state. When the auditor arrives, the answer is already in the system.
Compliance Is the Starting Point, Not the Destination
It is worth being clear about what compliance can and cannot do. Meeting ISO 27001, SAMA, NIST or DORA requirements shows that the right controls exist. It does not prove that they will hold under pressure.
The difference is the same one that separates compliance from resilience. Compliance asks whether the control exists. Resilience asks whether it works when you need it. A well-run compliance programme gives you the structure, and testing and measurement prove the capability.
That is why efficient compliance management matters. Every hour saved on duplicated paperwork is an hour that can go towards testing real recovery, closing real gaps and strengthening the organisation.
How autoResilience Supports Compliance Management
Spreadsheets can hold a control library for a while, but they struggle with mapping, reminders, evidence and reporting at scale. A connected GRC platform is built for exactly this.
autoResilience brings governance, risk, compliance and resilience management into a single framework. For compliance teams, it helps you:
- Link frameworks to policies and controls, so one control can support requirements across standards such as NIST, ISO 27001 and DORA
- Connect compliance with risk and business continuity, so you can see how a control gap affects critical services
- Automate workflows, including reminders, approvals and escalation for control owners
- Track findings and remediation to closure, with clear owners and deadlines
- Gain real-time visibility through a dashboard that gives leadership an objective view of compliance posture
The outcome is less duplication, fewer surprises at audit time and a clearer picture of what is working.
Frequently Asked Questions
What is multi-framework compliance?
It is the practice of meeting the requirements of several regulations or standards at once, such as ISO 27001, SAMA, NIST and DORA, usually by sharing controls and evidence across them.
What is a unified control framework?
It is a single library of controls mapped to the requirements of multiple frameworks. Each control is tested once and reused wherever it applies.
How does compliance automation help?
Automation handles repetitive tasks such as evidence reminders, approvals, control testing schedules and reporting, which reduces manual effort and the risk of missed deadlines.
How is continuous compliance different from annual audits?
Annual audits check compliance at a point in time. Continuous compliance monitors controls throughout the year, so gaps are found and fixed early.
See It in Action: Book an autoResilience Demo
If your team is managing several frameworks in spreadsheets, or dreading the next audit cycle, a short walkthrough can show you what a connected approach looks like.
Book a free demo and see how unified controls, automated workflows and real-time visibility can make compliance management lighter, clearer and more reliable.
Written by

Shambhavi Singh is a Marketing Executive at Ascent Risk & Resilience, where she contributes to brand communication, content strategy, and digital storytelling across the organization’s risk and resilience solutions. With a background spanning content writing, voice-over artistry, anchoring, public speaking, and social impact, she brings both creativity and clarity to every message she crafts.
Shambhavi’s passion for communication started early in her hometown of Varanasi, where her curiosity for culture and heritage shaped her worldview. A natural storyteller and confident speaker, she has built a strong presence as a social media writer and continues to use her voice to inform, inspire, and engage audiences.
Driven by a blend of will and skill, she is committed to building meaningful connections, leading with empathy, and contributing to initiatives that create positive change. A social worker at heart and a marketer by profession, Shambhavi combines creativity, purpose, and leadership in everything she does.